IBM · Cloud Pak for Data
Adding Pattern
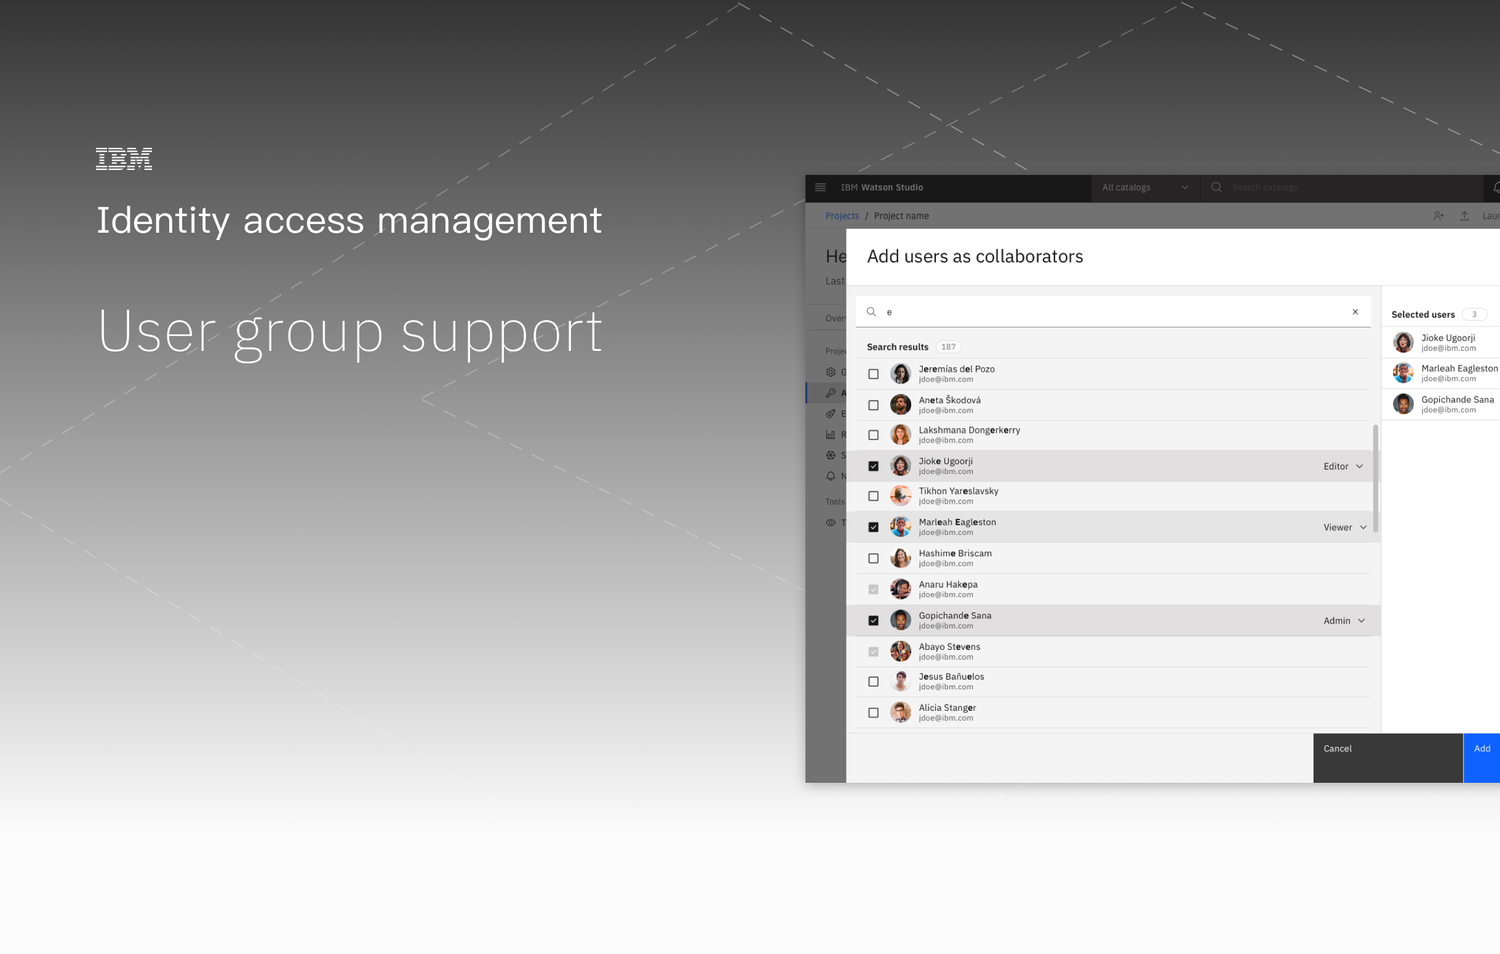
User groups and one adding pattern across the platform
Background
Cloud Pak for Data 3.5 introduced user groups, so every service could add user groups to its assets, such as projects and catalogs. When we synced with service teams, we found they each added collaborators differently for service-level access control. Our platform team raised this inconsistency and came up with an improved solution.
Design considerations
- Apply the ‘collaborator’ pattern across the Cloud Pak for Data platform
- Separate modals for users and user groups. Rationale: separate APIs; user groups are fewer, and used more in large environments
- Peek into user groups in separate, simple modals. Rationale: user groups can be large, and this avoids confusing interactions in the collaborators table
Problems
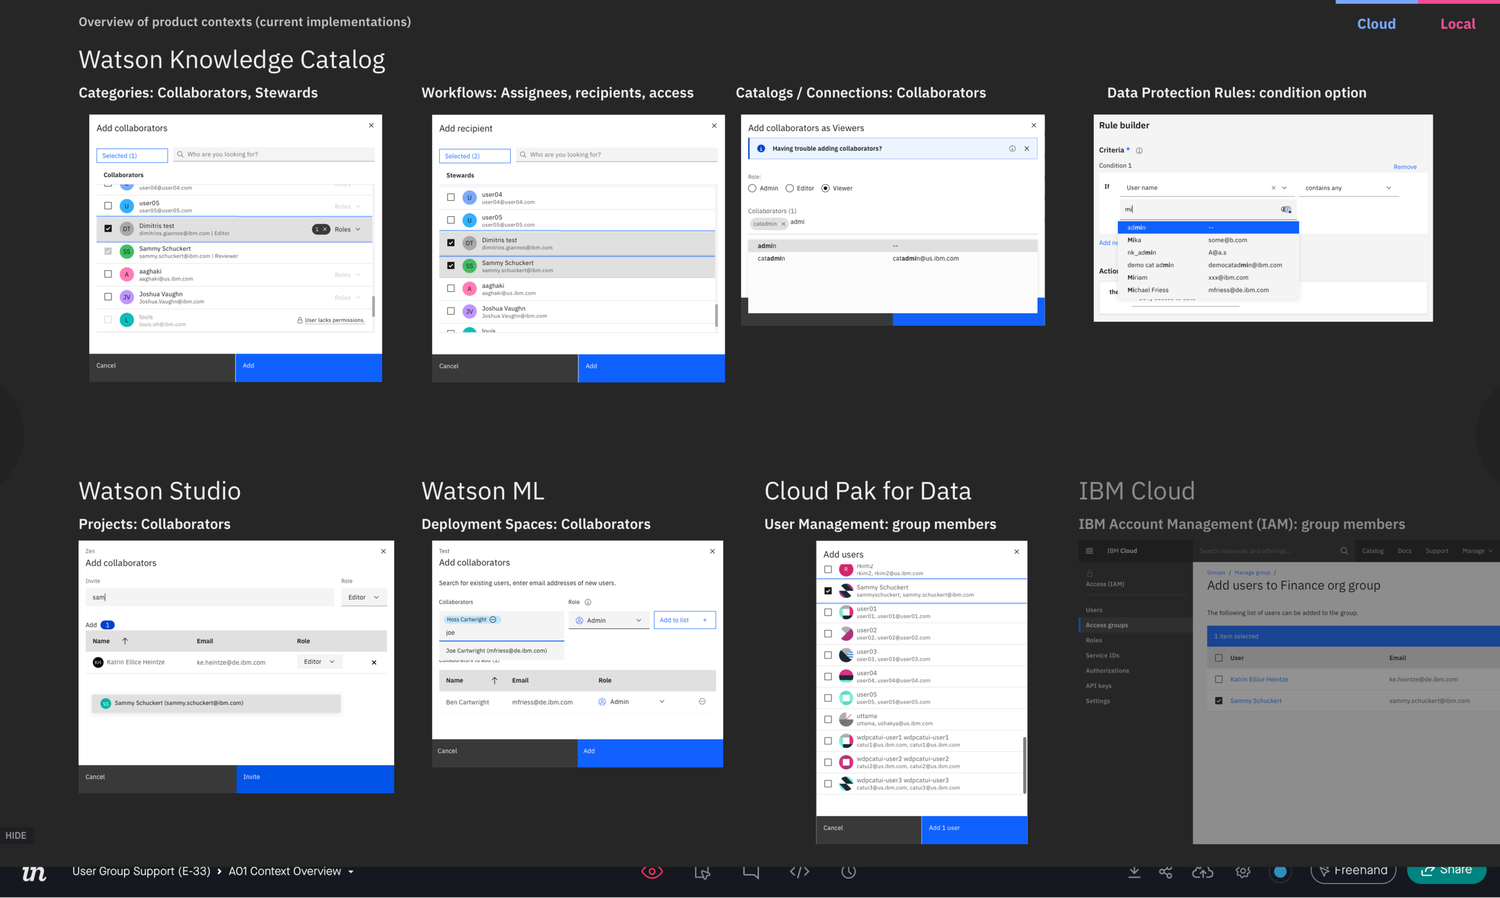
Different services used different patterns for adding objects, such as collaborators, stewards and assignees, both on-prem and in the cloud.
Design goal
Cloud Pak for Data end users should have one consistent way to add objects across the whole platform, on-prem or in the cloud.
As-is
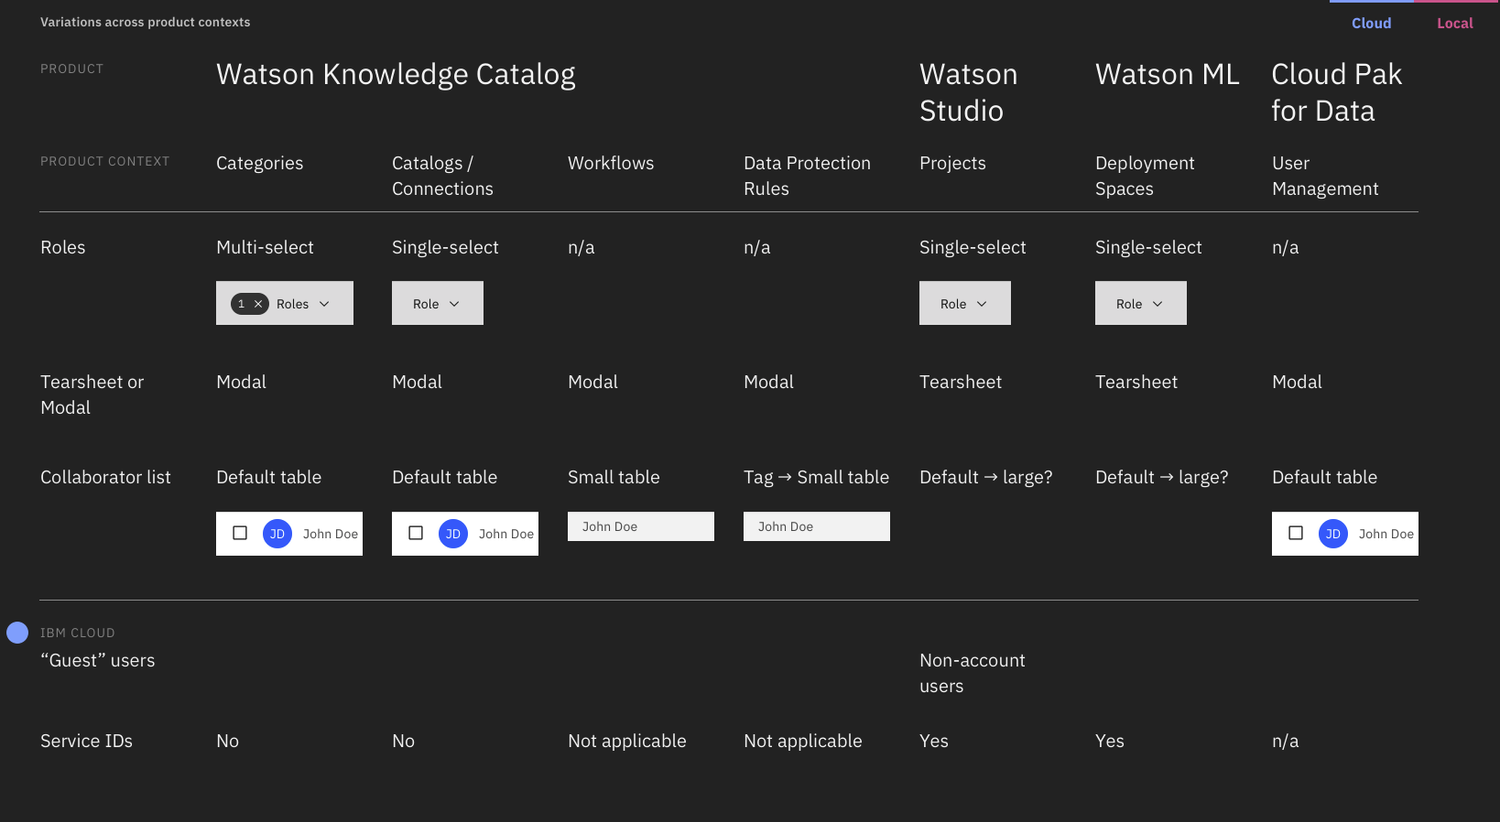
To design a common framework, we first had to understand how it varied across product contexts. We listed every component and compared them.
Design iteration
Since the pattern would be used across the platform, we synced with service teams weekly so they knew about every update. Meanwhile, we ran several rounds of usability testing to guide the iterations.
Outcome
We arrived at a basic framework that worked in every context, with some modifications for specific needs. We synced every design outcome with the stakeholders in the service teams and made sure it could be implemented both on-prem and in the cloud.